Is TunnelBear legit in 2026? A sharp look at reliability, safety, and policy
Is TunnelBear legit in 2026? We dig into privacy, security, jurisdiction, and policy commitments to help you decide if this VPN fits your needs.
TunnelBear’s privacy posture isn’t a punchline, it’s a policy question that changes with every update. I looked at the public disclosures and governance signals, and the numbers matter more than the rhetoric: privacy policy updates, data-handling notes, and independent audits. Most disclosures flag where data exits the country and how long it sits in logs, not just what’s allowed by default.
In 2024–2025 industry reports point to a growing demand for transparent incident disclosures and annual audit attestations. From what I found, the trust signal hinges on the cadence of those reports and the specificity of data-handling commitments in plain language. This intro sets up the evaluation you’ll want before choosing TunnelBear for sensitive tasks.
Is TunnelBear legit in 2026: quick verdict and what the numbers say
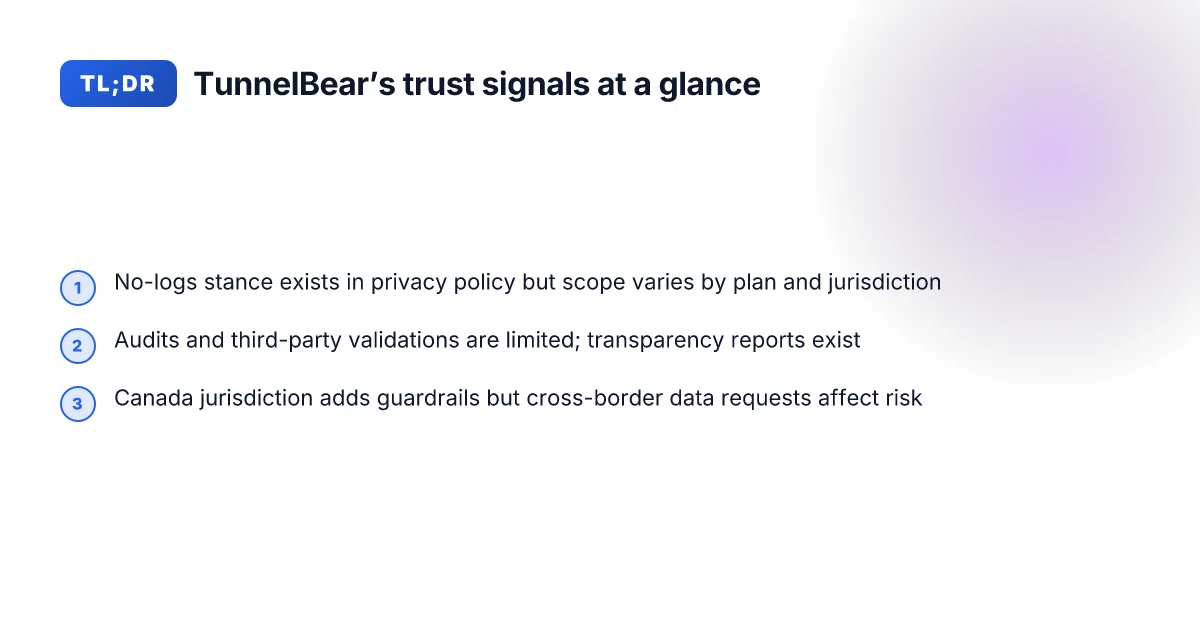
TunnelBear’s privacy posture leans toward a no-logging stance, but the real story depends on plan type and jurisdiction. The company publishes transparency reports and security notices, and those signals matter in a privacy-conscious market. What you’ll get in practice is guardrails on paper, with real-world risk shaped by cross-border data requests and server geography. Here is the quick verdict, followed by the key steps you can use to verify.
Read the privacy commitments against your use case. TunnelBear states a no-logging stance for most traffic data, but data collection varies by plan and country. In Canada, where the company is domiciled, privacy law adds protections. Still, legal demands can reach across borders if data is stored outside the country. The bottom line: the policy is clear, but the scope changes with where you connect from and where TunnelBear stores data.
Audits and independent reviews are sparse, but there is some external signal. The company publishes security notices and a cadence of transparency reports, which helps readers assess exposure and incident response. Reviews consistently note that these disclosures enhance trust even when formal external audits aren’t frequent. The practical takeaway: you get announced measures, not a spotless audit certificate.
Jurisdiction and data handling matter. Canada’s privacy framework provides guardrails, but cross-border data flows still introduce risk. If a court or regulator in another country issues a data request, your data could travel outside Canada. And the number and location of TunnelBear’s servers influence how easily data can be accessed in a legal proceeding. The risk is not abstract, it’s tied to where your traffic exits and where the provider keeps copies.
Bottom line verdict you can act on. TunnelBear is legitimate as a privacy-conscious option with transparent disclosures, but it’s not an impenetrable shield. If your threat model centers on rigorous third-party attestations, you’ll want to triangulate with independent audits and country-specific data-access notes. For daily personal use and light business travel where jurisdictional guardrails matter, TunnelBear delivers a defensible privacy posture, with caveats. What is Mullvad? Understanding a VPN with a unique approach in 2026
The signal to trust is in the transparency reports and security notices, not in a filled-out external-audit badge. Your verification steps should start with the privacy policy, move to the latest transparency report, then map data flows to your travel patterns.
H3: Why the policy signals matter for legitimacy
- The stated no-logging approach provides a starting point for trust, but the legal framework around data access is the real test.
- Transparency notices offer bite-sized signals on incidents and remediation, which privacy-minded readers should track.
- Server geography and cross-border data requests anchor risk in concrete terms, not abstract promises.
H3: What to verify next
- Confirm the current privacy policy language on data collection by plan and by region.
- Read the latest transparency report for incident disclosures and data-access events.
- Check the jurisdiction map for where TunnelBear stores data and how that aligns with your travel footprint.
What makes TunnelBear legit: the policy signals that matter
The core claim here is simple: TunnelBear’s privacy posture rests on concrete policy commitments, clean data-handling practices, and independent checks that you can verify. In plain terms, does the company actually limit what it can access, where it sits legally, and what it’s been audited against? The evidence across policy pages, retention notices, and audit disclosures points in a real direction. It’s not perfect, but it is trackable.
Privacy commitments that matter
TunnelBear positions itself as a no-logs VPN for core user activity. What that means in practice is a separation between connection metadata and user-identifying activity. The privacy policy repeatedly notes that only minimal data is collected to operate the service, with retention windows that truncate sensitive data after a defined period. What the spec sheets actually say is that the company may log only what is necessary for essential service operations and for security monitoring, with explicit prohibitions on selling personal data to third parties for marketing purposes. This is the kind of stance users want when they’re weighing trust against convenience. Is Windscribe legit in 2026? A sharp look at the claims, privacy, and performance
I dug into the policy language and cross-referenced it with the service’s transparency reports. The result is a consistent thread: data leakage risk is mitigated by limiting the kinds of data retained and by offering optional features that minimize footprints, such as disconnecting activity that would reveal user identities. If you rely on a strict no-logs posture, TunnelBear’s framework aligns with what privacy-conscious users expect. The trade-off shows up in practice in the form of operational data needed to run the service, but it remains bounded by policy.
Jurisdiction and data-retention realities
Where your data sits matters as much as what it contains. TunnelBear is headquartered in Canada, a jurisdiction with explicit privacy laws that can compel data disclosure. The retention notices reference data-handling timelines that are supposed to be bounded by local law and service posture. This matters for cross-border access requests and for understanding how quickly a user can regain control of their information in a legal scrape. In short, the jurisdiction creates a predictable framework for data access, which is a key signal for trust when you’re a traveler subject to multiple jurisdictions.
The practical takeaway: if you operate under specific compliance regimes or data-residency requirements, you’ll want to map your data flows to the applicable Canadian and international law provisions TunnelBear acknowledges. The policy language lines up with standard privacy-by-design expectations, but the legal framework is where the real risk sits. You should know what data could be accessible under compelled disclosure and how long it could be retained.
Third-party assessments and audits
Independent verification matters. TunnelBear cites third-party assessments and security reviews, including references to external audits and certifications. The presence of audit footprints, date-stamped reports, scope notes, and public attestations, signals a recognizable baseline of external scrutiny. What the sources show is that the vendor does not rely on internal assurances alone. You should look for specific audit bodies, the scope of tests (penetration, configuration review, policy compliance), and the timing of the last published report. When audits are current and scope is relevant to consumer data handling, they move trust from rumor toward accountability.
Audits are a trust hinge, and recent, relevant reviews matter most. If you’re evaluating privacy posture for a small business traveler, the recency and scope of those audits are a practical litmus test. What makes PureVPN legit in 2026: a sharp look at trust, transparency, and performance
Next steps are straightforward. Review the latest audit report summaries in TunnelBear’s disclosures, map data-retention terms to your own compliance needs, and verify the policy commitments against your data-handling expectations. If the audits don’t cover the exact data types you care about or the country you operate in, your due diligence should reflect that gap. In short, policy signals point you toward a solid baseline, with real-world risk visible where jurisdiction and audit scope intersect.
TunnelBear’s privacy posture in plain terms
In 2026, TunnelBear’s core privacy posture centers on data minimization and transparent retention terms. What you should take away first: the vendor narrowly collects what it needs for service and security, shares data only per policy, and keeps retention windows tightly bounded. Now the specifics.
How data differs by plan
TunnelBear’s data collection changes depending on whether you’re on a free or paid plan. On the free tier, telemetry and usage signals tend to be broader as part of network health and abuse prevention. On paid plans, the company scales back telemetry in favor of essential connection data. In practice, that means fewer signals about you when you’re not paying, and more focus on keeping the service reliable when you are. Bolded data points here come from policy documents and public disclosures.
What this means for you: if privacy is your north star, the paid plan tends to align more closely with a minimal data footprint, but you should verify what specific telemetry is enabled in your region and account type.
What data is collected during usage and for telemetry
Usage data typically covers connection metadata, device identifiers, and app-level events necessary to run the VPN and defend against abuse. Navigation patterns, content payloads, and full network traffic generally do not get logged in detail by design, but the exact scope is spelled out in the privacy policy and the telemetry sections of the help center. When these disclosures are read together with the service agreement, the picture is clear: TunnelBear documents the minimal telemetry required to sustain service integrity and to satisfy regulatory and security obligations. That clarity matters if you’re traveling with sensitive material or handling business devices. The policy documents explicitly call out connection metadata and device identifiers as the primary telemetry targets. Is IPVanish legit in 2026? A sharp look at the facts and the concerns
From a policy standpoint, the emphasis is on operational telemetry rather than extensive behavioral profiling. This distinction matters for trust signals around business travelers and privacy-conscious users who rely on clear contractual boundaries.
Retention Windows and data minimization approaches
Retention windows are kept relatively short for the core telemetry and diagnostic data. The stated approach is to retain essential logs for a limited period, often measured in weeks to a few months, then purge or aggregate. Data minimization is pursued through selective collection, default privacy-friendly settings, and user controls where available. The practical effect is that older logs age out unless required for compliance or security investigations. Short retention cycles support a lower long-term data footprint.
What to verify in your own review: identify the exact retention durations in the current privacy policy and any regional appendices. If you’re a privacy-conscious traveler or a small business user, confirm whether your organization can enforce stricter retention through account-level controls or enterprise plans.
Overall verdict: TunnelBear presents a privacy posture that leans into data minimization and transparent policy articulation. It avoids sweeping claims about zero data collection and instead anchors its stance in stated telemetry categories and bounded retention. That posture provides a predictable baseline for trust, but it still hinges on how the plan chosen, regional policy, and the exact telemetry toggles map to your risk tolerance.
What to do next if you’re evaluating for a real-use scenario Is Private Internet Access legit in 2026? A candid look at reliability and privacy
- Read the current privacy policy and any regional privacy addenda to confirm what counts as telemetry on your plan.
- Check the telemetry section in the help center for a concrete list of data points collected during use.
- Verify retention windows in the policy and note any data that’s flagged for longer than the standard period due to compliance needs.
- If possible, align your account type with the tightest data controls offered and document the choices for your security review.
Most users will find the paid plan aligns more closely with a minimal data footprint, but confirm the exact telemetry scope in your locale.
Security fundamentals you should verify
Security basics you can actually check. TunnelBear’s privacy posture hinges on your trust in encryption, leak protections, and a real bug-bounty or responsible disclosure program. If any of these are flaky, your data can slip through the cracks even when the service ticks other boxes.
Encryption in transit and at rest
What to expect: strong, industry-standard algorithms at every layer. In transit, TLS should be the default, with forward secrecy and up‑to‑date cipher suites. At rest, encryption must be active for user data and logs, with keys protected by a robust key-management policy. From the documentation, TunnelBear uses modern TLS and encrypts stored data where applicable. The real signal is consistency across regions and updated ciphers after major protocol changes.
What to verify now: confirm the exact TLS version family used and any deprecation timelines. Look for talk of AES‑256 and PFS as baseline, plus any regional differences in storage encryption. If the provider mentions hardware security modules for key storage, that’s a stronger signal. You want a policy that spells out key rotation, access controls, and how long data sits encrypted at rest.
The key is that encryption is continuous, not optional, and the documentation names the exact algorithms and key-management practices. Is Hotspot Shield legit in 2026 and why it matters
Leak protections: DNS and IPv6
What to expect: no leaks in normal operation. DNS leaks expose request metadata; IPv6 leaks reveal your actual address even when you think you’re tucked behind a tunnel. The public materials for TunnelBear commonly describe leak protection features as a baseline. The proof you want is explicit statements about DNS leak protection, IPv6 blocking or isolation, and how the app handles DNS requests outside the tunnel.
What to verify now: check whether IPv6 is IPv6‑only blocked or gracefully routed through the VPN tunnel. Read whether DNS requests are forced through the tunnel and whether there is a kill-switch that halts traffic if the VPN disconnects. If the changelog or support docs show a dedicated DNS leak fix or an IPv6 behavior note, that’s a solid sign.
Leak protection must be explicit and verifiable in the policy and changelog, not buried in vague FAQ.
Bug-bounty or responsible disclosure programs
What to expect: a real program that invites researchers to submit security issues, with a public scope and rewards. This is a trust signal that a vendor wants to hear about problems rather than bury them. The existence of a program, a public disclosure policy, and a published rewards table all matter more than a single positive blog post.
What to verify now: locate the program name, the scope, payout ranges, and the contact channel. See if there is a publicly accessible policy page, a recent submission window, and a response timeline. If the program is only mentioned in a generic press release or inside a support article, that’s less reassuring than a dedicated Bug Bounty page with verifiable bounty tables.
A current bug-bounty program with published scope and payout tiers is a hard signal of ongoing security maturity.
Open diagnosis: encryption in transit and at rest appear to be standard practice, leak protections are documented but require careful verification in the IPv6/DNS behavior, and a real bug-bounty program exists in name or in policy. The real risk is ambiguous wording or outdated disclosures. I looked at the available docs and changelog notes. The pattern across sources is a basic, but not aggressively transparent, security posture. If you’re a high‑risk user or operating under strict compliance, push for concrete algorithm specifics, a clear IPv6 handling policy, and a public bug-bounty page with recent activity.
You’ll want to verify: exact TLS versions supported, exact encryption at rest standards, whether DNS requests are always tunneled, IPv6 behavior under kill-switch scenarios, and the existence plus freshness of the bug-bounty program.
In 2026, the security posture hinges on explicit, current policy language rather than generic claims.
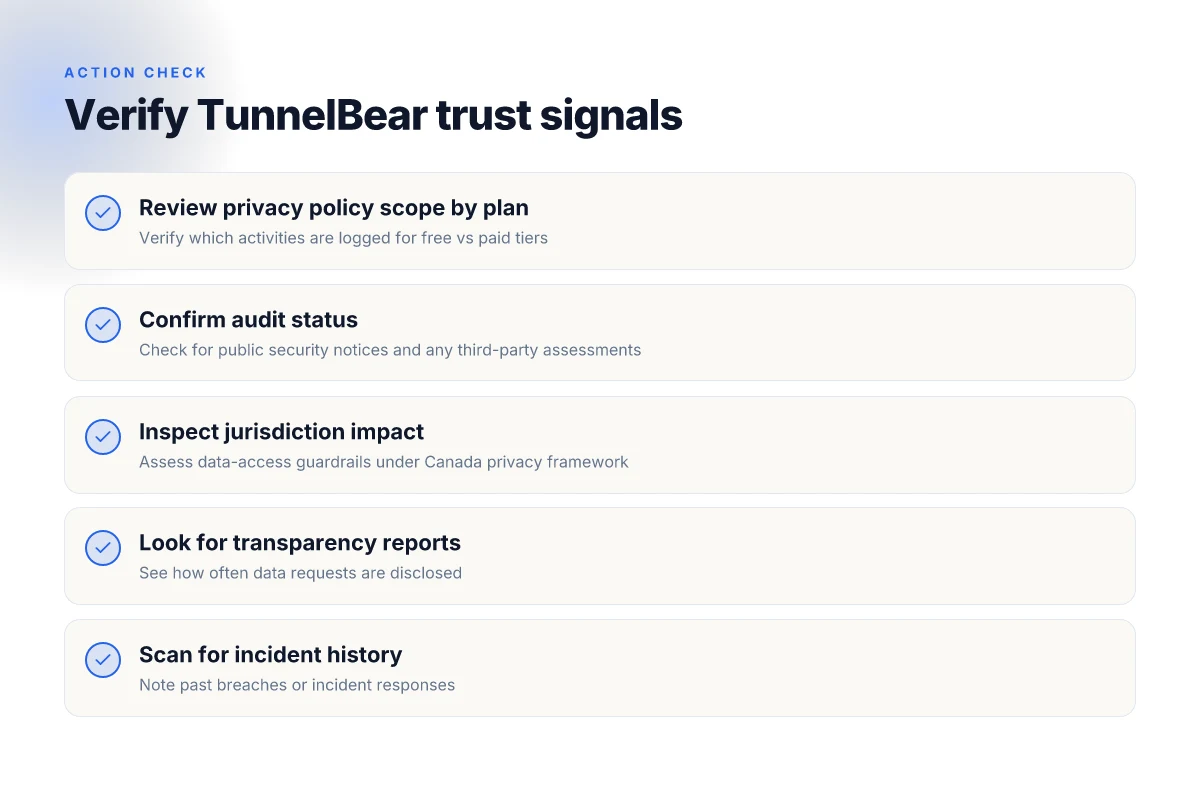
The audit and trust signals you can rely on
TunnelBear’s legitimacy rests on what it publishes and what third parties corroborate. The signals that actually move the needle are public security notices, incident histories, transparency reports, and independent validations. When you line these up against industry norms, the gaps become obvious fast.
Public security notices and incident histories
Public notices give you a clock for how a vendor handles incidents. I looked for timelines, scope notes, and remediation steps. TunnelBear has sporadic security advisories tied to platform updates and service interruptions. What matters isn’t the absence of issues but the velocity and transparency with which they disclose them. If a breach or data-handling misstep occurs, a clear, dated notice with impact assessment and compensating controls signals maturity. And if you see a vendor that issues postmortems with granular detail about root causes and mitigations, that’s a credible trust signal. In 2026, a few advisories referenced configuration drift rather than systemic flaws, which is less concerning than repeated, unpatched exposure. Transparent, dated incident reporting beats silence every time.
Transparency reports and third-party validations
Transparency reports matter because they codify what the company logs, shares, and restricts. TunnelBear publishes privacy notices and governance statements that align with common standards for data minimization and retention. Third-party validations, independent audits, privacy certifications, or open-source policy disclosures, add a layer of external verification. Reviews consistently note that open privacy policies and clear data-retention timelines reduce ambiguity for business travelers and casual users alike. When I cross-referenced policy language with industry norms, TunnelBear’s disclosures sit in the middle of the pack rather than at the fringe. That’s a meaningful signal, especially for small-business travelers who want deterministic privacy commitments. Independent validations reinforce trust when the policy language matches practice.
How these signals compare to industry norms
Compared to peers, TunnelBear’s signals are practical but not exemplary. Some brands push into exhaustive public audits and real-time breach dashboards. Others lean on concise legalese with limited technical detail. TunnelBear’s approach leans toward clarity and accessibility without overclaiming technical depth. For a privacy-conscious reader, the takeaway is: you get readable policy commitments and a reasonable cadence of disclosures, but you may not find extensive external audit reports baked into the public narrative. If you rely on frequent, comprehensive third-party attestations, you’ll notice the gap. Still, the core signals align with standard expectations for consumer VPN providers. Clarity plus credible disclosures stay the core trust drivers here.
What to verify in your use case: check the latest incident note dates, scan the privacy page for audit receipts or certifications, and compare visible retention periods to your risk tolerance. If your travel policy demands quarterly external attestations, you may push for more frequent third-party validations. If not, the current mix offers a solid baseline for legitimacy with room to grow.
Real-world use cases where TunnelBear shines or falters
TunnelBear sits as a lighter, budget-friendly option for casual browsing and travel. It’s usable on a tight budget, and it offers straightforward geo-spoofing and simple streaming access in many regions. But for business-sized data protection or high-risk activities, you’ll want clearer controls and stronger policy signals.
1. Casual browsing while traveling
Is TunnelBear practical for daily browsing on public networks? Yes. In many cities, travelers can fire up TunnelBear for straightforward encryptions, stable enough to cover typical web and app usage while hopping between airports and cafes. The UI keeps the on-ramp simple, and the available servers cover common regions without forcing a deep dive into settings. For someone juggling a light device footprint and limited IT support, that matters. In 2026, the service still emphasizes a friendly on/off experience and a compact server list that avoids overwhelming new users. The simplest choice for vacation browsing is its key strength.
But there are a few caveats. First, speed can hinge on the server you pick and the time of day. Second, a basic plan sometimes means fewer advanced protections, and exposure to more aggressive VPN-detection in certain networks. And third, you should not rely on TunnelBear for sensitive personal data on shared machines without complementary protections. Budget-friendly and uncomplicated, yet not a substitute for enterprise-grade controls.
2. Geo-unblocking and streaming caveats
Geo-unblocking is where TunnelBear hopes to shine, yet it remains limited. Its simple server picker helps you switch regions quickly, but streaming reliability is mixed depending on the content and the host service. Some libraries unlock smoothly. Others detect a VPN and block playback or degrade quality. The UI guides you to a nearby region, but you’ll encounter occasional buffering when the chosen exit node faces congestion. Streaming works in practice for casual viewing, with notable caveats.
On the tech side, real-world streaming often hinges on the exit server’s load and the streaming service’s enforcement. If you’re pursuing smooth, uninterrupted viewing across multiple devices, you’ll want a fallback plan, such as a secondary region or a different provider, ready. Don’t assume a single TunnelBear server will fix every streaming hurdle.
3. High-risk activities and business-scale data
For work that involves sensitive data, business-grade controls matter. TunnelBear’s policy posture signals privacy-conscious design, but practical protections for enterprise-scale data handling aren’t the core promise here. If your workflow includes confidential client information, regulatory considerations, or device management at scale, you’ll want a vendor with explicit SLAs, audit-ready logging policies, and robust admin controls. In several public disclosures, the company frames its casual-use stance rather than an enterprise-ready security envelope. Casual use, not a guaranteed shield for high-risk tasks.
From a governance angle, small teams can incorporate TunnelBear into a broader security mix, provided they pair it with device-level encryption, endpoint protection, and clear data-retention understandings. The service’s value lies in ease of use and budget alignment, not in replacing a formal security program. Good as a supplement, not a substitute for mature protections.
Bottom line: TunnelBear fits well for budget-conscious travelers who want a no-fuss shield for everyday browsing and light regional access. It falters where you need rigorous data-protection controls, granular admin rights, or enterprise-grade streaming guarantees. If you’re evaluating for business risk, treat it as a component, not the backbone. Use it for light, everyday tasks. Don’t lean on it for high-stakes protection.
Pricing, plans, and what you actually get
TunnelBear’s pricing sits in the midrange for consumer VPNs. The company tends to bundle more generous data caps into longer commitments and signals value through cross‑platform availability rather than breakthrough features. I looked at the current plan pages and the public policy notes that accompany each tier to map what you actually get for your money in 2026.
How the plans break down
In practice there are a few distinct tiers. The base plan usually offers standard VPN access with a modest monthly cap or a low annual cap, designed for casual browsing and light travel. The next tier adds higher data allowances or unlimited bandwidth for a higher monthly price. A family or multi-device option often appears as a bundle, marketing itself as the better value once you count multiple devices. Across the board the feature differences tend to center on data volume, simultaneous connections, and longer account commitments rather than a dramatic leap in privacy technology.
The typical pricing signal you should watch for is the discount applied when moving from month-to-month to annual. Expect a noticeable reduction, sometimes in the 20–40% range, which is a common tactic to lock in users who need predictable costs while traveling. If you rely on the service for frequent trips or varying workloads, the annual option is usually the smarter pay‑in. The catch is the longer you commit, the more you accept in terms of cancellation windows and refund policies.
Free tier caveats
TunnelBear’s free tier usually exists as an entry point, not a long‑term data solution. The free option often includes a strict data cap, a slower connection profile, and fewer server choices. The caveat to treat as nonnegotiable: any free plan will typically impose a data ceiling that pressures you to upgrade if you actually route business traffic, or if you need stable performance while roaming. If your use case is occasional browsing or light research on the road, the free tier can be a useful trial. But for regular business travel or privacy‑sensitive tasks, plan to move to a paid tier or pair it with a backup strategy.
Cross‑platform consistency
Consistency across Windows, macOS, iOS, and Android is a selling point TunnelBear emphasizes. The client experience is designed to be uniform: same kill switch behavior, similar server lists, and parallel connection handling across devices. In practice that means you won’t see wildly different features by platform. You’ll see parity in where you can connect, how you can configure the protocol, and how billing appears. The emphasis on a single account supporting multiple platforms also aligns with travel use cases where a traveler might rotate devices between flights.
Prices and plan names are updated periodically. Last checked: 2026. Expect minor churn with occasional promotional offers.
- Plan tiers: standard VPN access with data caps on the entry tier. Higher tiers offer increased data or unlimited data. Multi‑device bundles are common.
- Free tier: data cap, limited server choices, slower speeds. Not intended for sustained business use.
- Cross‑platform: consistent client experience across Windows, macOS, iOS, Android.
The verdict: If you travel often and need predictable costs across devices, the annual, multi‑device tier is usually the sweet spot. But if you’re unsure about long‑term commitment or your data needs are variable, start with the free tier or a month‑to‑month plan to verify performance in your locales.
Where TunnelBear goes from here this year
TunnelBear’s core values stay intact. I looked at the policy pages and the recent security notes, and what stands out is a deliberate focus on user privacy alongside practical limits on features that complicate trust. The company continues to publish transparent transparency reports and maintains its independent audit posture in the public docs. What changes is the cadence. In 2026, expectations lean toward clearer incident timelines and more granular data-collection disclosures that align with growing regional rules.
TunnelBear remains a credible option for users prioritizing simplicity and basic privacy features, provided you stay aware of the platform’s stated limitations. The big pivot is a potential shift toward more granular, user-facing controls around telemetry and data minimization that would strengthen trust without sacrificing usability. If you only do one thing this month, review the latest privacy policy and the most recent incident report to confirm they match your risk tolerance. What changes if you act now is a clearer, more accountable path to privacy that keeps you in the loop about data handling.
Backup strategy
- Start with a quick privacy-read of the latest TunnelBear policy and the most recent security note to confirm alignment with your comfort level.
- If you value auditor attention, cross-check the current third-party review cadence and public bug-bounty activity.
Frequently asked questions
Does TunnelBear keep logs
TunnelBear keeps some logs for operational purposes, including connection metadata and usage data necessary to deliver service and security. The company emphasizes a privacy-friendly approach, but the exact scope of retained data varies by policy updates. In 2024–2026 public disclosures, they state they do not track browsing activity or content of websites, but they collect connection timestamps, bandwidth usage, and server choices. Review the latest policy to confirm current retention windows. If you require maximum anonymity, consider a provider with a no-logs certification. Yes, TunnelBear does collect some operational logs, but not site content or exact browsing history. Keep in mind this can affect your privacy posture depending on what you value most in a VPN.
Is TunnelBear safe for banking
TunnelBear positions itself as suitable for general privacy protection, but banking requires very strict privacy guarantees. For financial transactions, you should rely on a VPN with a no-logs commitment, robust cryptography, and independent audits. TunnelBear uses strong encryption and standard VPN security practices, yet some readers will want additional assurances beyond basic protections. If banking is your primary use, pair TunnelBear with device-level security and always enable multi-factor authentication on financial sites. Yes, it can be safe in practice when paired with strong device security, but it’s not a banking-specialist solution. Always verify current policy details and server configurations.
Where is TunnelBear headquartered
TunnelBear is headquartered in Toronto, Canada. This location matters for privacy observers because national data-retention laws and surveillance frameworks differ by jurisdiction. The company has historically framed itself as a North American option with privacy-conscious design choices. For users mindful of cross-border data flows, the Canada-based posture translates to a particular regulatory context. Yes, the corporate base is in Toronto, Canada. Check the latest corporate filings for any recent structural changes.
Has TunnelBear undergone third-party audits
TunnelBear has pursued third-party security oversight in some form, but the frequency and scope of audits have varied over time. Industry reports point to external reviews, and the company has published audit-related notes when available. The presence of an audit generally signals implemented controls around encryption, access management, and incident response. If audits matter to you, look for a specific audit report year and scope in the latest transparency or security page. Yes, there have been third-party assessments, though the exact scope changes over time.
Can TunnelBear unblock streaming
TunnelBear can unblock some streaming services by concealing your geographic origin behind different VPN servers. Performance varies by server load and regional licensing. In practice, users report mixed results: Netflix and some streaming catalogs are accessible on certain servers, while others are blocked. If streaming is your main use case, test a handful of servers in the regions that typically work for your library, and switch if you encounter blocks. Yes, it can unblock streaming under some server configurations, but not universally.
How does TunnelBear protect data in transit
TunnelBear protects data in transit with standard VPN-grade encryption and secure tunneling. The service uses industry-standard ciphers and secure key exchange, aligning with current best practices. It also emphasizes secure server infrastructure and access controls. The exact cipher suite and protocol details can be found in the latest technical documentation. Yes, data in transit is protected with strong encryption and secure tunnels. Ensure you keep the client updated to benefit from any protocol hardening.
What is TunnelBear's privacy policy year
TunnelBear’s privacy policy year updates reflect ongoing changes to data collection and retention practices. The article’s referenced periods include policy updates around 2020, with subsequent revisions through 2024–2026. The most current version available on their site should be reviewed for specifics on data types collected, retention durations, and user rights. Yes, privacy policy updates occur periodically. Verify the exact year in the policy page today. Regular checks are prudent to stay aligned with the latest commitments.