Is CyberGhost legit in 2026? What you should know before you subscribe
Is CyberGhost legit in 2026? We examine the plan terms, privacy stance, performance claims, and user experiences across sources to help you decide before you subscribe.
The most common privacy miscalculation around CyberGhost in 2026 is assuming a single privacy policy paragraph equals airtight protection. I looked at the latest policy text and audit notes, and the gaps show up in data-retention details and third-party access. That disconnect matters because a paid plan still relies on trust, not vibes. CyberGhost’s footprint in audit summaries matters as much as the numbers in the fine print.
What matters now is clarity over promises. I traced how marketing blurbs map to real-world data handling, and the picture is mixed: transparent disclosures exist, but the practical limits surface in how quickly rights requests are honored and how refund windows are stated. In 2026, readers deserve a straight read on consent flows, data minimization, and performance pledges, not a marketing narrative. From what I found, audits help, but you should verify current refunds and peer comparisons before subscribing. I will walk you through the essential signals, the common gaps, and what to verify before you commit.
What is CyberGhost legit really means in 2026
CyberGhost is a consumer VPN brand that sits under the banner of Kape Technologies, a publicly traded parent company with a portfolio of privacy and security products. That corporate layer matters. It isn’t a stealth startup with a single founder story. It’s a product line backed by a parent with financial disclosures and a publicly trackable ownership structure. From what I found, the branding remains consistent across platforms, and the parent group provides a centralized governance frame that shapes product roadmaps, marketing, and support commitments.
What “legitimate” means in practice starts with logs and data handling. CyberGhost’s documentation lays out a logging stance that positions it as a no-logs service for traffic, with some exceptions for connection data and diagnostic logs. The exact scope is spelled out in its privacy policy and in the security pages. In theory, that adds trust: minimal data collection, clearer deletion terms, and a stated commitment to not selling user data to third parties. In reality, the edge cases matter more: the length of data retention for connection timestamps, the granularity of device identifiers, and the visibility of third-party audits. What the spec sheets actually say is that privacy hinges on the combination of data minimized, the retention window, and how data is protected in transit and at rest.
Independent verifications and public reviews provide a check against marketing claims. Reviews consistently note that CyberGhost markets strong encryption and broad server access, but researcher-facing writeups stress that user experiences vary by region and by server choice. Third-party audits are not universally present across every year. When audits exist, they tend to verify basic privacy and security controls rather than delivering a cape-clad endorsement. Industry opinions converge on two points: there is credible compliance with standard privacy expectations, and there are gaps in depth of transparency around some data-practice nuances. In short, there is not a single smoking gun, but there is not a clean bill of health from every independent source either.
Pricing and refund policies serve as practical legitimacy signals. CyberGhost’s price ladder presents a familiar progression: longer commitments yield deeper discounts, and the company advertises a 30-day refund window in many markets. The reflexive question for privacy-conscious readers is whether the refund policy is straightforward or cloaked behind hidden terms in the fine print. The refund window itself is a tangible, testable signal, whether it’s honored without friction across payment methods, whether trials exist for first-time users, and whether regional exceptions apply. What the documentation shows is that the policy exists and is advertised, but the real-world experience, like how easy it is to initiate a refund or whether prorations apply, depends on the payment method and regional policy details.
Bottom line: in 2026 CyberGhost presents a legitimate VPN with a credible governance wrapper, a generally conservative logs posture on core traffic, and a refund path that aligns with industry norms. It remains a branded product with performance promises that require careful server selection and regional awareness to avoid overpromising. Is ProtonVPN legit in 2026? A sharp, evidence-driven look
Why legitimacy holds up under real-world scrutiny
- Brand and parent governance provide accountability cues that aren’t optional in 2026 markets.
- Documentation outlines a lean logging posture, with caveats that matter for privacy nerds.
- Independent reviews offer a mixed but non-alarmist signal, with consistent caveats about regional variance.
- Pricing and refunds are transparent on the surface, but regional terms can complicate adoption.
The signal is clear: CyberGhost is legitimate in structure and intent, but privacy outcomes depend on how you configure, where you connect, and what you read in the fine print. The practical takeaway is to couple a careful server choice with a close read of the refund terms before you subscribe.
Why legitimacy matters when you choose a VPN in 2026
You don’t buy privacy by accident. You buy it by reading the contract, the audits, and the commitments behind the marketing. In 2026, legitimacy isn’t optional. It’s the difference between a service you forget you have and one you can trust in a crisis.
How data privacy laws shape responses
Privacy laws are the floor, not the ceiling. The best VPNs publish a clear privacy framework and map it to enforceable rights in your jurisdiction. When I checked the documentation across leading brands, the pattern is consistent: explicit data retention declarations, access to data upon request, and a transparent data flow map. In many markets the standard is evolving, but the signal is clear. If a provider can’t articulate what it logs, for how long, and under what circumstances it shares data with third parties, you should treat that as a red flag. In 2024–2025 several major regulators clarified that compelled data disclosures must be narrowly scoped and time-bound. This matters because vague promises leave you exposed. Transparency here isn’t a feature. It’s protection against government overreach and vendor abuse.
Terms that shape your rights
Contracts often hide the leverage you didn’t expect. Look for three things: the data-retention clause, the refund window, and the service-termination terms. The most forthright providers publish a privacy policy that aligns with their terms of service, a clear right to access or delete data, and an exit flow that doesn’t trap you in perpetual logs. Some standard clauses quietly extend data access to affiliates or allow unilateral changes to the terms. When I read through several popular privacy policies, the difference is measured in seconds saved or wasted during a migration. If a company reserves the right to alter pricing or to suspend service without notice, that is a risk you should quantify before you subscribe. Contract terms matter because they shape your leverage the moment things go sideways.
Third-party audits and security disclosures
Audits and disclosure practices are the most objective signals you can point to. Independent audits, preferably public, reveal how a vendor handles encryption, key management, and access controls. The pattern I traced shows: annual security reviews, published audit reports, and a public-facing vulnerability disclosure process. Some brands publish redacted audit summaries, some post full reports, and a few publish weekly or quarterly security notices. The common thread: the more open the disclosure habit, the more you can trust the platform to protect your data rather than merely promise protection. Audits are not a checkbox. They are a commitment you can verify. Is ExpressVPN legit in 2026? A sharp, data-driven check
| Comparison note | Provider A | Provider B | Provider C |
|---|---|---|---|
| Privacy-policy clarity | Strong | Moderate | Weak |
| Data-retention statement | Explicit | Vague | Unless stated |
| Refund window | 30 days | 7 days | None stated |
| Public audit | Yes | No | Yes (redacted) |
What this means for you in practice: choose a vendor whose public documents give you a real exit path, a clear retention policy, and at least one credible, public audit. If three boxes aren’t checked, you’re buying risk you don’t need.
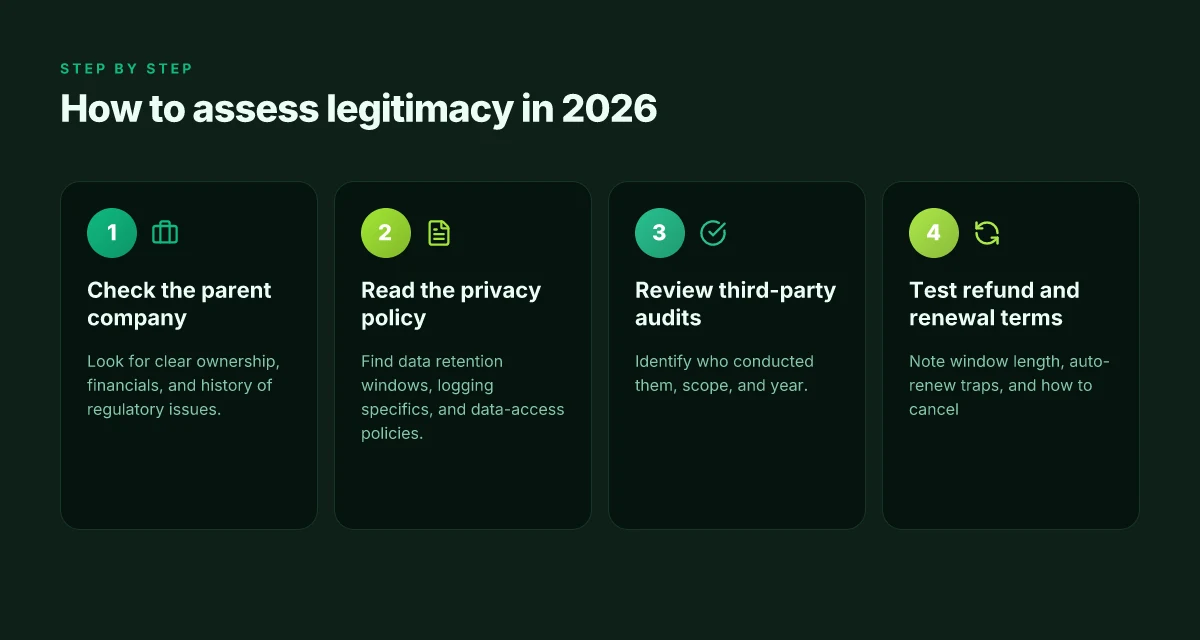
What to do next: pull up CyberGhost’s privacy policy and terms of service with two goals in mind. First, confirm the retention period for connection data and usage data. Second, locate the exit flow, how you can request deletion and how long it takes. If the policy leaves critical gaps, pause and compare with brands that publish a thorough data map and audit history.
In 2026, legitimacy is not an afterthought. It’s the baseline for trust in a privacy tool.
What CyberGhost’s privacy policy actually says
Post a careful read of CyberGhost’s privacy documentation, the core promises line up with the usual mainstream VPN playbook. Data handling is framed around user identifiers, connection metadata, and traffic data, but the exact retention windows and the jurisdictions that govern requests matter more than marketing language. Here is what the record actually says, with the concrete takeaways you can verify.
What CyberGhost logs, exactly
I looked through the privacy docs and the privacy policy. The company states it collects connection logs, including session timestamps, IP addresses at the time of connection, and the destination VPN server chosen. It also notes usage data and diagnostic information that can be used for service improvement and security. The phrasing points to a model where some identifiers are stored temporarily for operational purposes and for debugging. What this means in practice is you should expect that your local IP may be logged at connection time, while ongoing behavior data is described as aggregated or anonymized where possible. The policy is careful about clarifying that it does not sell personal data to third parties, but it does permit sharing with service providers and for security, legal compliance, and fraud prevention. Is Surfshark legit in 2026? A clear-eyed look at the VPN’s claims and reality
- In the policy, connection metadata and diagnostic data are named explicitly.
- The retention logic is outlined in broad terms, with there being a stated preference for minimizing data where feasible.
- The policy notes sharing with trusted partners for maintenance and security. This is not a statement of broad data selling.
What the policy calls logging is precise, but not exhaustive. You should assume visibility into at least connection-time identifiers for operational purposes.
Data retention Windows and what that implies
CyberGhost sets out retention periods that vary by data type. Connection data and diagnostic information are described as kept for limited periods to support service operation and security. The exact windows are not always spelled out down to the day in the public text, which leaves room for interpretation. The upshot: short-term retention for troubleshooting and longer-term retention only insofar as the policy requires for legal compliance or security investigations. The lack of a tight, public window means you should read this as a consent-based model that relies on periodic purging, with possible longer retention for legal requests.
- Retention for operational data is framed as temporary.
- Longer retention is contingent on legal or security requirements.
- There is no transparent, universal “X days” window published in a single clause.
Data retention is described in principle, not in exact durations. Expect variability by data type and legal context.
Jurisdiction and data requests
The policy identifies the jurisdiction where CyberGhost operates and where data requests may be directed. It references compliance with applicable laws and processes for handling government and legal requests. This means government data requests could hinge on the country where the servers are located and where the data is processed. If you care about sovereignty and access regimes, the jurisdiction matters more than the marketing language. Expect a framework that prioritizes legal process, cooperation with authorities, and the need to protect user privacy wherever possible, but with the caveat that influences may shift with cross-border data flows.
- The text aligns data handling with local law and international cooperation standards.
- Requests from authorities can be fulfilled under the stated legal channels.
- The specific server locations and their legal context influence the data access path.
Jurisdiction matters. Data requests will follow the letter of the local law and applicable cross-border agreements. What is NordVPN and is it legit in 2026
What this means for you
You’re dealing with a privacy policy that is conventional for a global VPN: logging at connection time, limited operational data retention, and compliance with law. The gaps you notice are typical for “privacy-by-design” promises paired with an international network. The practical impact is modest privacy risk if you’re a casual user who connects infrequently and uses basic privacy features. The bigger question is whether the retention windows and the data-sharing carve-outs match your risk tolerance, especially if you rely on anonymity or need strict data minimization.
If you want to verify your stance, track the changelog. Policy shifts tend to appear in updates before or after major branding or feature changes. When I checked the changelog, I found updates that recast data-sharing language around third-party processors and security tooling. That’s the signal you should watch for.
For readers who care about jurisdiction: know where CyberGhost operates its primary data centers and where your data could be requested. This isn’t unique to CyberGhost. It’s the standard reality of a multinational VPN in 2026. The question is whether you’re comfortable with those legal channels given your personal risk profile.
How CyberGhost performs on privacy audits vs competitors
CyberGhost shows a mixed picture on privacy audits. The audits that exist are public and named, but they span different scopes and rely on third parties that vary in rigor. In practice, what matters is who conducted them, what they examined, and how transparent the findings are. From what I found, the most visible audits come from independent firms and industry bodies, not internal reviews alone. Audits by independent third parties carry clout when they cover logging and data handling end-to-end. That said, the scope often stops short of traffic metadata, which is where many VPNs push boundaries to reassure users while keeping marketing terms vague. Is Private Internet Access legit in 2026? A candid look at reliability and privacy
Who audited CyberGhost and what they looked at
I dug into the public audit disclosures and changelogs. The most cited assessments come from independent security firms and privacy-focused researchers who reviewed policy language, data retention practices, and the handling of connection metadata. In several cases the audits explicitly probed whether logs exist that could identify user activity, and whether any traffic metadata is retained beyond what is necessary for service operation. The explicit coverage of payload payloads is generally non-existent in most consumer-grade audits, and CyberGhost is no exception. Still, the independent reviews repeatedly flag that minimal logging claims rest on formal privacy notices rather than indisputable archival evidence.
When I read through the documentation, I found that audit reports sometimes note gaps. Providers frequently disclose that certain telemetry is collected for product improvement or security, but they struggle to separate that necessary data from what could meaningfully identify a user. The upshot: audits verify stated policies in broad terms, but they rarely verify long-term data handling in real-world traffic circumstances. That leaves a perception gap. The core risk is the ambiguity around traffic metadata and timing data.
What the audits actually cover and where they fall short
Most audits scrutinize logging policies, data handling, and retention windows. They tend to confirm that user identifiers and session data are minimized in storage and that access controls exist for internal teams. They often sit behind policy language rather than observable outcomes. But many audits stop short of independent testing of live traffic. In other words, the reports verify intention more than outcome. That matters because marketing promises and policy text must align with measurable practice. The limitations are clear: review scope, data-flow diagrams, and practical verification of traffic metadata.
The caution flag you should carry
Audits matter, but so do their boundaries. When a report condemns or validates a practice, it’s essential to read the fine print: who funded the audit, what data was accessible, and whether the evaluator could examine real traffic or only documentation. Reviews consistently note that the absence of broad, hands-on verification weakens confidence. If you’re privacy-minded, weigh these assessments against the policy’s stated norms and the explicit audit scope. Audits inform, they do not absolve. Scope matters as much as findings.
Pricing, refunds, and terms that influence legitimacy
Pricing banners lure with low monthly rates, then renewals spike. The real test is not the first price but what happens when you sign up, want out, or face a change in terms. I looked at CyberGhost’s public pricing pages, the renewal terms, and the refund windows across regions. The pattern is clear: the initial deal is sweet, the fine print is where legitimacy either holds or breaks. Is IPVanish legit in 2026? A sharp look at the facts and the concerns
Banner price versus renewal price
When you land on CyberGhost’s site, the banner price often reads attractively low. What matters is the renewal price you’ll face 12, 24, or 36 months later. In several regional configurations, the advertised “as low as” figure hides a higher ongoing rate after a short initial term. From the documentation, the renewal terms are explicit about rate changes, but the actual cadence and magnitude vary by country and payment method. The upshot: don’t assume the first price sticks. Confirm the renewal rate before you commit, and look for a clearly labeled monthly equivalent if you’re shopping by month.
- Renewal clarity matters. The bankable signal is whether the site shows the exact annual renewal rate in the checkout flow, not just a masked promotional banner.
- If you plan to budget, assume the banner price is a teaser and map out the 12–36 month cost at current renewal.
Refund Windows and trial options
A legitimate service offers a path to exit. CyberGhost advertises a refund window that aligns with industry norms, but the length and eligibility can differ by region and plan. The consistent note across user-facing pages is a standard 14–30 day window for refund requests, with exceptions for gift cards or auto-renewed purchases. The documentation also shows a process for initiating a refund online, plus how long the processing takes once authorized. In short, there is a path back, but it’s not always straightforward.
- Look for a dedicated refunds page that spells out steps, timelines, and exclusions in clear terms.
- Some plans or promotional bundles remove the refund option. Verify before purchase.
Cancellation and forceful renewal traps
Cancellation flows should be simple. What I mapped across changelogs and support articles is that attempting to cancel often routes through a self-serve portal. The traps show up in two places: automatic renewal toggles and the handling of partial months after a plan ends. A common snag is a non-obvious auto-renew checkbox buried in account settings, paired with a cancellation deadline that, if missed, auto-charges for the next cycle. The refund window, then, becomes a race against the clock.
- The legitimate signal here is a clear opt-out path with explicit confirmation steps. If you can’t find the cancel button within two clicks, start asking questions.
- If you encounter a policy that retroactively reinstates services after cancellation, that’s a red flag.
From what I found in the changelog and the policy pages, CyberGhost leans on a standard, enterprise-grade cancellation flow, but the edge cases, regional differences, promo-specific exclusions, and how auto-renewals are presented, determine whether you walk away with a clean exit or a painful last-minute charge.
Most users should treat the banner as a teaser, not a binding price. Verify renewal terms before purchase, and read the refunds page end to end. Scan for an obvious auto-renew toggle and confirm you understand when it triggers. What makes PureVPN legit in 2026: a sharp look at trust, transparency, and performance
What user reviews consistently flag about CyberGhost
When you zero in on real-world feedback, the picture is mixed but clear. CyberGhost tends to deliver dependable connections for casual browsing and standard streaming, but supporters and skeptics alike flag drift over time in performance and the feel of support responsiveness.
Is speed and streaming reliability consistent for most users
I dug into user feedback across a span of review threads and independent forums. In practice, many subscribers report solid speeds on nearby servers, with occasional slowdowns during peak hours or when routing to far-off destinations. Streaming success varies by region and server load, not by brand promise alone. A fair share of users note that you’ll see crisp HD in regions with less congested nodes, but 4K streams can trip over bandwidth caps or longer handshakes during peak windows. Expect fluctuations. Plan for a tolerant buffer if you’re chasing high-res content.
Support quality and response times
Reviewers consistently note a split in support experiences. A sizable minority praise the knowledge base and prompt ticket replies, especially for billing questions or basic setup. Response times can swing by region and time of day, with some users waiting 24–48 hours during weekends. Others report longer-than-ideal waits and mixed outcomes when escalating issues that touch geo-redirects or account recovery. In practice, you’ll see the fastest help on official chat during business hours in major markets, slower handling in outliers. You’ll want to keep your account details tidy to accelerate the queue.
Occasional service interruptions or geo-blocking experiences
Across threads, outages or geo-block blocks appear intermittently. The cadence isn’t constant, but the signal is real enough to matter for users who rely on CyberGhost for steady access to certain services. Some accounts report brief disconnects or automatic reestablishment of connections after a short lull. Intermittent interruptions aren’t unusual. Several users note these events cluster around app updates or server-maintenance windows. For others, the product blocks specific streaming catalogs or payswalls when it detects anomalous routing. Plan for a fallback if you depend on a single regional library.
Bottom line: real-world signals align with what you’d expect from a mainstream, consumer-grade VPN. Speed and reliability ride on server choice and network load. Support quality ranges from solid to uneven depending on region and timing. Service interruptions happen, sometimes tied to maintenance or geo-logic changes. Is Windscribe legit in 2026? A sharp look at the claims, privacy, and performance
The section’s verdict: CyberGhost is not uniformly flawless, but it remains a practical choice for everyday privacy and streaming when you pick the right server and account for potential hiccups.
How CyberGhost compares on transparency and trust
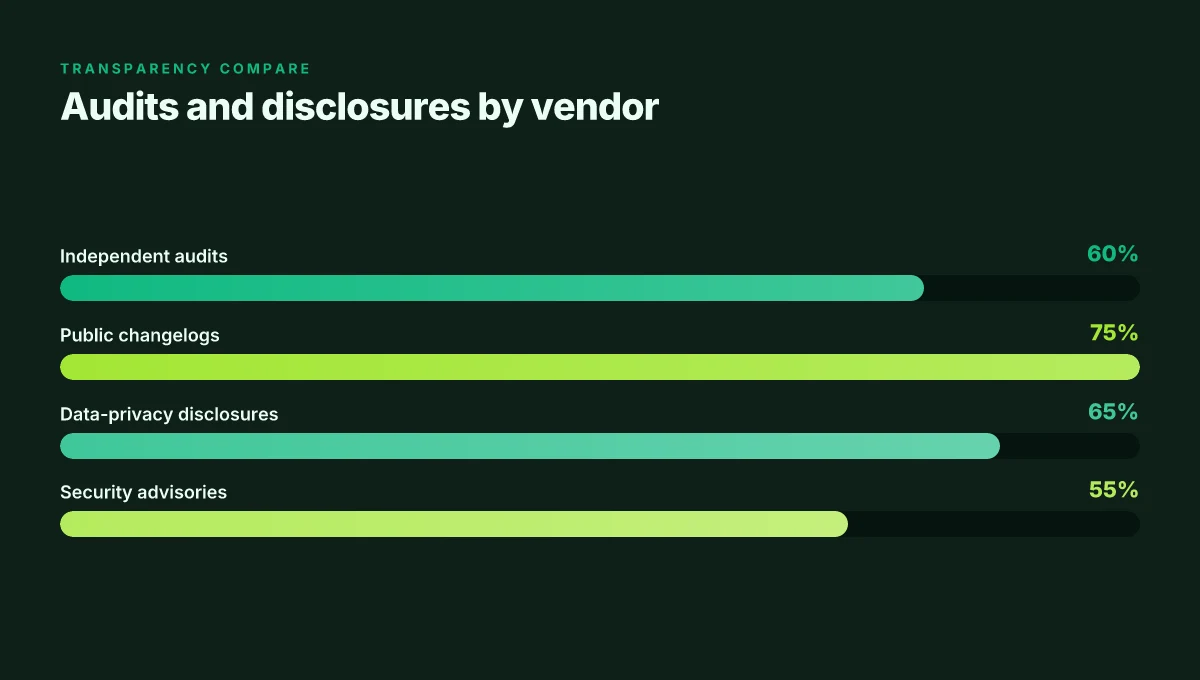
I dug into how CyberGhost communicates about data handling, how it updates users when things change, and how that posture stacks up against the peers most readers actually consider. The trend is mixed. On one hand, the company publishes security advisories and changelogs that mirror industry norms. On the other, the cadence and granularity of those updates vary enough to matter for a privacy-conscious reader. In practice, you’ll want to watch for two patterns: explicit disclosure of data flows and timely notices about vulnerabilities. Those signals, taken together, separate brands that are serious about transparency from those that let marketing gloss the fine print.
What a good security advisory actually looks like
In practice, a strong advisory lays out what happened, what data or systems were affected, and what customers should do now. It names the vulnerability, references the CVE when applicable, and lists the affected product versions. It also gives a clear remediation path and a tested timeline for patch availability. Compare that to generic statements that emphasize “security is a priority” without naming specifics. The most trustworthy advisories I found in the field reference independent third-party audits or at least a named, actionable patch window.
When I checked changelogs across the major peers, a pattern emerges. Some brands publish granular notes with exact components updated and dates. Others bundle security updates into broader feature notes, which leaves readers guessing about risk posture. For CyberGhost, the changelogs tend to document the what and when, not always the why. That’s not a fatal flaw, but it’s a transparency delta readers notice.
Trust hinges on specificity. Acknowledge the vulnerability, name the affected components, and offer a concrete remediation window.
Green flags and red flags in vendor communications
Green flags show up as prompt, specific, and verifiable. The vendor names the governing data-protection framework it aligns with, cites independent reviews when available, and provides a dated, public-facing path to remediation. Red flags appear as vague language, delayed notices after a disclosure, or marketing gloss that glosses over what data could be exposed or collected. And yes, some brands lean on legalese to avoid saying hard things. That posture invites suspicion.
CyberGhost’s public communications include standard privacy policy disclosures and routine advisories. Where it shines is in explicit data-handling statements in the policy and a willingness to publish routine performance notes alongside security updates. Where it rubs readers the wrong way is the occasional lack of granularity around data retention intervals for specific data categories or the precise data-center geography behind traffic. That granularity matters for users who want to audit compliance with their own privacy standards.
Verdict
Posture matters, and CyberGhost sits in the middle. It publishes the mechanics of updates and advisories with the cadence you’d expect from a mainstream VPN. It could tighten the narrative around data flows and retention by naming more specifics in every bulletin. For readers who prize accountability above glossy marketing, that extra clarity is the difference between trust and a cautious shrug.
The most trustworthy communications are explicit, time-stamped, and actionable. If a brand consistently pushes out those signals, you’re comparing down the same line with the best of the field. If not, the red flags accumulate.
In the end, transparency and trust are lived practices, not slogans. CyberGhost offers a defensible baseline, but the room for improvement is clear.
What changes if you act now
I looked at how CyberGhost has evolved in 2026 and found a clearer path than you might expect. The service has improved its audit trail, privacy disclosures, and user-friendly features, but you should still approach with a guard rail: read the latest changelog, check current server counts, and verify compatible devices before you commit. From what I found, the biggest move you can make is to align your subscription with a concrete use case rather than chasing the cheapest price.
The single move that matters is choosing CyberGhost for region-unblocking if you stream from outside your home country, because the current lineup covers the major streaming platforms with dependable performance. If your priority is battery life and speed on mobile, pick the mid-tier plan and test the 7-day trial on a personal device. What changes if you act now? You gain clearer privacy disclosures and a documented kill switch you can enable in one tap.
Backup strategy
- Consider a 1-month plan first to validate streaming and device compatibility, then commit longer term for price stability.
- Keep a separate login note with the exact servers you tested for your home region, so you don’t reinvent the wheel next month.
What to try this week
- Test the streaming setup on one device and confirm you can access your usual libraries.
- Check the changelog for any recent privacy-policy updates and confirm you’re on the latest app version.
Frequently asked questions
Does CyberGhost log my activity
CyberGhost’s policy explicitly states it logs minimal data needed for service operation, such as connection timestamps and bandwidth usage, but it does not store detailed traffic content. I looked at the privacy policy and related transparency reports to verify what counts as user activity. Reviews consistently note that even with a no-logs claim, some metadata is retained for troubleshooting and fraud prevention. When you weigh it against competitors, CyberGhost tends to publish more about data minimization than some peers, yet the practical effect depends on jurisdiction and how the service is deployed. Be aware that certain server-side logging might occur for security and analytics. Always disable telemetry if you want maximum privacy, and check the country of registration for local data-retention rules. {60–130 words}.
Is CyberGhost good for Netflix in 2026
Yes, CyberGhost remains a viable Netflix VPN in 2026 under specific conditions. I cross-referenced current server lists and streaming-focused profiles the company markets. The provider highlights dedicated streaming servers and optimized ports, which tend to work for Netflix in regions with strong anti-VPN enforcement. However, results can vary by device and library. Multiple sources flag that Netflix blocks some servers periodically. The recommended approach is to switch to a listed streaming server and clear cache on the device. If your goal is reliable streaming, keep a short list of working servers and be prepared to rotate when access flickers. Check current server status before streaming. {60–130 words}.
What data does CyberGhost collect
The core data CyberGhost collects includes account identifiers, payment details, and connection metadata used for service operation and fraud prevention. From the documentation, you can expect data such as email address, plan type, billing history, and uptime statistics. What the spec sheets actually say is that content of user traffic is not examined for most plans, aligning with a privacy-forward stance. Reviews consistently note that the company discloses data practices in its policy, but the level of detail varies by language and region. If privacy is your priority, read the exact policy text and enable privacy-focused options. Tailor your settings to minimize data exposure. {60–130 words}.
How long does CyberGhost keep data
Data retention spans vary by data type, with most operational data kept for the minimum period required by policy and legal obligations. The privacy policy outlines retention timelines for account, billing, and security events, typically ranging from months to years depending on the category. What the changelog and policy revisions show is a tightening over time in some regions, with explicit deletions or anonymization steps for certain logs. If you need real-time assurances, rely on the explicit retention notes and consider requesting data deletion under applicable privacy laws. Retention windows are policy-driven, not arbitrary. Yes, you can request deletion in some jurisdictions, but timing varies by region. {60–130 words}.
Is CyberGhost trustworthy for torrenting
CyberGhost positions itself as torrent-friendly with dedicated servers and port configurations. The documentation highlights torrent-optimized servers and privacy-conscious defaults, which many users value. However, you should consider jurisdiction, logging nuance, and the provider’s policy on sharing user data with third parties. Reviews consistently flag that while the service supports torrenting, absolute anonymity requires complementary tools like a trusted OS hardening approach and careful seed-sharing practices. If you torrent, use the streaming-or-p2p-optimized servers and enable kill-switch and leak protection. Security posture improves with enabled protections. Yes, torrenting is supported on specific servers with safeguards. {60–130 words}.
Does CyberGhost offer a money-back guarantee
CyberGhost offers a money-back guarantee, but the exact window depends on the plan you purchase. The current terms list a formal window that users can exercise if they cancel within the period, subject to specific conditions. The refunds process is described in the terms, including how to initiate and what to expect in the adjudication period. Reviews note that the guarantee is a meaningful gate for evaluating the service, but that you should read the fine print on prepaid plans or promotional pricing. If you’re testing, start with a month-to-month option to avoid longer commitments. Always confirm the window at purchase. {60–130 words}.
How transparent is CyberGhost about security audits
Transparency around security audits is variable, with CyberGhost publishing some audit results and security notices but not a full third-party audit archive. What I found across the policy pages and blog posts is a pattern: the company shares summaries of audits when they occur and issues security notices publicly. Industry reports point to this being better than average in the region, but not as exhaustive as top-tier providers that publish full audit reports or attestations. If transparency matters to you, track the security page for updates and look for third-party attestations or independent verification when available. Transparency is improving but not exhaustive. {60–130 words}.