Is ProtonVPN legit in 2026? A sharp, evidence-driven look
Is ProtonVPN legit in 2026? I trace the company’s privacy promises, logging policies, and third-party reviews to separate signal from noise. A concise, evidence-backed verdict.
A single privacy promise can still hide a practical gap. When you map ProtonVPN’s disclosures against its actual data-retention notes, the mismatch is smaller than you fear yet not negligible, privacy ethics meet corporate reality in real time. Is ProtonVPN legit in 2026? The gap between policy and practice is where readers should focus. ProtonVPN promises strong defaults, but the fine print matters.
I looked at ProtonVPN’s policy changes in 2024–2026, cross-checking audits and jurisdiction notes from multiple sources, including official statements and independent reviews. The result: a pragmatic read on transparency, governance, and risk for travelers and small teams who need trustworthy governance without surrendering usability. What changes between promise and practice matter most in 2026. The takeaway: transparency isn’t a pure yes or no, it’s a spectrum you can map against your risk tolerance.
The plain definition of is ProtonVPN legit in 2026
ProtonVPN markets itself as a privacy-first VPN rooted in Swiss jurisdiction and a no-logs claim. In 2026, that definition sits at a moving axis: corporate privacy commitments, actual data-retention and telemetry practices, and signals from regulators or independent auditors. My read is simple: ProtonVPN remains a privacy-forward option, but the field has evolved and trades some promises for different controls elsewhere.
Corporate privacy commitments ProtonVPN’s core pitch is straightforward: privacy is a product feature, built into the company’s structure and governance. The Swiss base matters. Swiss privacy law offers strong protections, and Proton’s ownership and governance align with that ethos. They publish a transparency stance and a policy framework designed to limit data collection. But a policy is not a shield by itself. When I read through the documentation, the emphasis is on minimizing data exposure and stripping service telemetry that could reveal user activity. The practical question is whether the policy evolves with product features and if changes require explicit user consent. In a crowded market, that clarity buys trust.
Data-retention and telemetry practices in practice What the spec sheets actually say is one thing. What the telemetry stack collects in practice is another. ProtonVPN’s no-logs claim leans on a design that does not retain session data or traffic content. Yet, the company does operate telemetry for service health, performance, and account integrity. The critical fork happens here: can telemetry be de-anonymized or merged with other data points? Reviews consistently note that ProtonVPN restricts data collection compared with some peers, but there are caveats. For example, authentication tokens and minimal connection metadata may exist to support billing and fraud prevention. This is not unique in the VPN space, but the tension between privacy commitments and telemetry realities is where trust audits and regulator signals matter most.
Third-party signals and regulator footprints External signals matter. Independent audits and third-party reviews, when available, provide ballast for the no-logs claim. In 2026 the landscape includes a broader set of certifications and more frequent governance disclosures than a few years ago. Industry reports point to a growing expectation for verifiable privacy controls and incident transparency. ProtonVPN has tended to publish governance updates and changelogs, which readers can use to cross-check claims. The signal here is mixed but leaning toward accountability rather than blind trust. You should track any new audit reports or regulator interactions as they surface.
Bottom line: ProtonVPN remains a legitimate privacy-focused option in 2026, especially for users who prize jurisdiction and a minimal-data posture. It sits among peers that trade off different models of transparency and telemetry. If your risk model emphasizes Swiss-law privacy and a clean no-logs narrative, ProtonVPN still fits. If you want aggressive telemetry boundaries or real-time regulator attestations, you may prefer rivals with deeper audit footprints. In short, legitimacy is robust but not absolute, watch for updates to audits and policy disclosures. Is ExpressVPN legit in 2026? A sharp, data-driven check
What to watch next
- The next moves in third-party audits and any new regulator-facing disclosures.
- Any shifts in telemetry kept for service health and abuse prevention.
- How ProtonVPN aligns with evolving privacy standards across the EU and UK post-Brexit landscape.
ProtonVPN remains a solid privacy option in 2026, but ongoing audits and disclosures will determine long-term trust. Trust hinges on verifiable no-logs assurances and transparent data practices more than hype.
How ProtonVPN works in practice for privacy
ProtonVPN’s privacy posture hinges on three claims you should verify in practice: strong encryption, a no-logs stance, and the integrity of the client not leaking data. In real-world use, the effectiveness of these claims depends on the subscription tier, the protocol choices available, and whether the client protects against DNS and WebRTC leaks. The truth is that promises become practice only when you can verify these moving parts in your own setup.
What you get with core features
ProtonVPN publishes robust encryption as a baseline. The service supports modern ciphers and VPN protocols, with multi-hop options that route traffic through more than one exit node. The theory is clean: more hops and strong crypto equal better privacy. In practice, you want to confirm two knobs before you decide to rely on it for sensitive work. First, the available protocols and their defaults. Second, whether multi-hop is optional or forced in certain configurations. If your workflow requires single-hop for latency, you’ll need to understand how that trade-off affects privacy.
From what I found in the documentation, ProtonVPN emphasizes a no-logs stance. The company repeatedly states that it does not log user activity or connection metadata beyond what is necessary for service operation. That distinction matters because a later legal demand could hinge on what data was collected and retained. Reviews consistently note that the no-logs claim is central to ProtonVPN’s value proposition, but it relies on governance and data-handling practices that evolve with policy updates. Is Surfshark legit in 2026? A clear-eyed look at the VPN’s claims and reality
Verifying privacy posture in practice
To verify privacy posture, you should check three things at minimum: your subscription tier, the protocol options you enable, and whether the client leaks DNS or WebRTC data. The ProtonVPN client provides several protocol choices, including modern options designed to reduce leakage risk. If you enable a protocol that prioritizes speed over privacy, you may compensate by turning on features like multi-hop and DNS protection. The subscription tier matters because more advanced features (like multi-hop) may be restricted to higher tiers. If you’re using a lower-tier plan, you may not have the same privacy controls, which changes the risk calculus.
DNS leaks are the classic blind spot. When I checked the changelog and product docs, ProtonVPN repeatedly frames DNS leak protection as built-in and enabled by default in recent clients. Nevertheless, a misconfiguration or a newly introduced feature toggle can silently reintroduce leaks. WebRTC remains a trickier frontier. A misconfigured browser or an active WebRTC export can reveal your IP even when the VPN is connected. The prudent move is to run a quick check after you install or update the client, then recheck after major app changes.
Protocol choices and app behavior matter
The protocol choices and app behavior are central to whether ProtonVPN lives up to its privacy goals. The default settings may favor compatibility and speed, but privacy is a function of explicit configuration. If you rely on multi-hop, confirm that both hops are active and that both exit nodes belong to the ProtonVPN network rather than third parties. If you suspect any behavioral drift after a version update, revisit the protocol matrix and the DNS/WebRTC protection toggles.
The practical takeaway is simple: dial in multi-hop and DNS protection, pick a protocol that emphasizes privacy over raw speed, and verify IP/DNS/WebRTC behavior after every client update.
| Decision point | What to check | Why it matters |
|---|---|---|
| Protocol choice | Enable multi-hop; select Privacy or Tor-enabled routes if available | Strengthens privacy when exit nodes are more diverse |
| DNS protection | Ensure DNS leak protection is on; run a test after install or update | Prevents your DNS requests from leaking outside the VPN tunnel |
| WebRTC handling | Disable WebRTC leaks in browser or via client options | Stops IP exposure through browser fingerprints |
| Tier awareness | Confirm feature access matches your plan | Privacy controls can be tier-locked; gaps create risk |
Verdict now: ProtonVPN’s privacy posture holds up when you actively configure multi-hop, enforce DNS/WebRTC protections, and choose a protocol with privacy as a priority. What is NordVPN and is it legit in 2026
What this means for you
- Solo travelers: enable multi-hop when possible, verify DNS protection, and watch for WebRTC leaks on public networks.
- Small teams: map your privacy needs to the tier that unlocks multi-hop and strong protocol options. Document a standard setup for everyone.
- Privacy-minded readers: treat the client as a wallet for policy choices. Your visibility into settings equals your control over risk.
Next step: confirm your current ProtonVPN configuration by reviewing the protocol you’re using, the presence of DNS protection, and any WebRTC leakage flags. Then run a targeted check after the next app update to ensure the posture persists. Action: document the exact settings you enable and capture a quick IP/DNS/WebRTC test snapshot for your records.
Why ProtonVPN matters in the privacy toolkit
In 2026, ProtonVPN sits at the edge of personal privacy and corporate transparency. Its Swiss base, paired with explicit commitments around limited data retention and open-source elements, shapes a risk calculus for readers who treat privacy as a live obligation rather than a theoretical ideal. I looked at the policy documents, the transparency reports, and the Swiss legal framework to map what actually follows promises.
What matters most in practice is not the marketing claim but the governance mix. Swiss privacy law bars blanket data collection, and Proton’s own disclosures put those limits into action. That combination narrows the surface area for data exposure when you’re traveling with sensitive work or handling personal identifiers on public networks. When I read through the latest transparency notes, I see a pattern: minimal retention, explicit data-handling choices, and a willingness to publish agent-level requests. In other words, the framework tends to push risk away from the user and toward a clearer, auditable paper trail. That matters in 2026, because the landscape has shifted from a “trust us” posture to “show me the logs.”
H3 Why ProtonVPN aligns with Swiss privacy law Is CyberGhost legit in 2026? What you should know before you subscribe
- Swiss law constrains mass data collection and gives users a clearer set of redress options. Proton’s disclosures consistently note limited data retention and anonymized data handling where possible, which reduces the risk of operational exposure during incidents.
- Reviews from privacy reporters emphasize that the Swiss jurisdiction adds a layer of accountability that’s harder to replicate in other regions. The combination of jurisdiction plus Proton’s public-facing transparency creates a more robust baseline for risk-averse users.
H3 Proton’s openness versus open-source elements
- Compared to mass-market VPNs, ProtonVPN often appeals to users who want minimal data trails and verifiable software provenance. The company’s emphasis on open-source components for certain clients and configurations gives reviewers something tangible to audit. This isn’t a pure trust exercise. It’s a verifiability game.
- Industry observers point to the presence of public changelogs and verifiable release notes as a signal that the product team treats transparency as a feature, not a marketing line.
H3 Real-world adoption surface and price friction
- The real-world usage surface includes onboarding friction and tiered pricing that shape adoption. Proton’s onboarding flow can feel more deliberate than the “one-click” experience offered by some competitors, and the price ladder reflects a philosophy that privacy is a steady, ongoing commitment rather than a cheap add-on.
- For solo travelers and small teams, the pricing strategy often makes sense when you value policy transparency and Swiss-law protections. Yet the entry point remains higher than the most aggressive mass-market providers, which affects who actually signs up.
From what I found in the changelog and policy disclosures, ProtonVPN’s legitimacy rests on a careful balance. It bets on jurisdictional protections, a transparent governance model, and a product design that favors reproducible privacy checks over mass-market convenience. The result is a tool that earns trust among users who weigh legal clarity and open-source credibility as much as speed or price.
The verdict is nuanced: ProtonVPN is legitimate as a governance-led, privacy-forward option for users with sensitive needs. It delivers on transparency and jurisdictional protections more consistently than many peers, but it requires acceptance of a somewhat higher onboarding friction and a pricing path that mirrors its privacy-first stance. If your risk model prioritizes verifiability and Swiss-law assurances, ProtonVPN deserves a close look. If you need ultra-fast onboarding at rock-bottom price, you’ll want to compare alternatives that trade some openness for speed and breadth.
What reviewers consistently note about ProtonVPN
ProtonVPN is often framed as privacy first, with governance built around transparency and user rights. Reviewers repeatedly flag that the company’s structure and public commitments align with a privacy-centric stance more than most peers. You won’t have to read between the lines to sense a deliberate separation between policy rhetoric and real-world practice. In many reviews, the governance model and the transparency disclosures sit at the core of the credibility claim. Is Private Internet Access legit in 2026? A candid look at reliability and privacy
I dug into how independent outlets frame the tradeoffs. Several reviewers praise ProtonVPN for its open approach to governance and data handling. The Swiss parent company’s privacy posture, including independent audits and public changelogs, recurs as a reliable signal rather than a nice-to-have. What this looks like in practice: clear privacy commitments, documented policy updates, and a trackable history of governance decisions that reviewers can point to when questions arise about data handling.
On the speed front, reviews consistently note a tension. Some outlets flag higher absolute speeds on certain networks, but they also emphasize that ProtonVPN’s configuration surface is more complex than the simpler apps favored by casual users. The friction here isn’t cosmetic. It reflects deeper choices about available protocols, multi-hop options, and split tunneling granularity. In other words, you get more knobs to turn, and that comes with a steeper learning curve. The upshot: faster potential speeds for power users, with a steeper onboarding for newcomers.
Policy disclosures and changelogs matter. Reviewers treat ongoing transparency as a proxy for ongoing legitimacy. What the spec sheets actually say is reflected in real-world cadence: frequent policy updates, clear rationale for changes, and accessible changelog entries that tie back to the privacy promises ProtonVPN publicizes. When a reviewer checks the latest update, they’re looking for alignment between what’s stated in the policy, what’s listed in the changelog, and how those choices affect user rights in practice. This triad becomes a proxy for trust when regulatory scrutiny looms.
Lead with the practical verdict. If you’re privacy-minded and prepared for a deeper setup, ProtonVPN often earns credibility by its governance narrative and the consistency of its disclosures. If simplicity and ultra-low friction are your priorities, expect the configuration to feel heavier than some consumer-focused rivals. The reviewer consensus is not a single line. It’s a spectrum that tilts toward trustworthiness in governance, with a clear caveat about onboarding complexity.
The best signal you can rely on is a consistent, date-stamped history of policy updates and changelogs. That transparency is the lever that turns promises into practice, or at least into traceable accountability. Is IPVanish legit in 2026? A sharp look at the facts and the concerns
Why governance and transparency matter in 2026
ProtonVPN’s governance model and the cadence of disclosures are what separate it from a purely marketing-driven VPN. Independent reviewers repeatedly highlight this as the core credibility vector. The explicit tie between policy updates, changelog entries, and user impact is not decorative. It’s the evidence reviewers use to judge ongoing legitimacy. For travelers and small teams, that means you can trace how a policy tweak affects data handling, rather than relying on vague assurances.
In short, reviewers consistently note that ProtonVPN’s privacy-first positioning holds up because the company makes its governance observable. The flip side is a steeper learning curve and more hands-on configuration. If you want the least friction, look elsewhere. If you want verifiable governance, ProtonVPN remains a credible option in the 2026 privacy toolkit.
Evidence checklist: does ProtonVPN keep logs?
ProtonVPN’s no-logs claim remains its strongest credibility signal. But the proof sits in the details. Reviewers call out the Swiss jurisdiction, and the changelog and privacy policy are where verification lives. In practice, no-logs is a selling point, yet operational nuance matters: what data is actually collected, when it’s retained, and how it’s audited.
1. The credibility signal: no-logs in a Swiss frame
ProtonVPN’s no-logs promise sits at the intersection of policy and geography. Switzerland’s privacy stance is a compelling backdrop, and multiple independent reviewers flag this as a credibility anchor. The core assertion is simple: ProtonVPN does not log user activity that could be tied to an individual, beyond what is strictly necessary for service operation and support. The Swiss data-protection regime strengthens the default shield around user activity. In theory, that combination should deter broad-scale data sweeps or opaque disclosure.
From what I found in the documentation and reviews, the Swiss framework helps. But the “no logs” banner does not immunize a provider from all data collection. Operational telemetry, authentication events, payment metadata, and connection metadata may exist in some form. The critical question is whether ProtonVPN’s policy explicitly limits linking network activity to a user, and whether data retained for operational needs is minimized and time-bound. What makes PureVPN legit in 2026: a sharp look at trust, transparency, and performance
The no-logs claim is credible on paper. The real test is what’s actually retained and for how long. The Swiss law supports minimal data retention, but policy language matters as much as jurisdiction.
2. Primary sources of verification: changelog and policy
What the spec sheets actually say is that no-logs is a core selling point, but the proof rests on primary documents. The changelog is the best place to spot any deviations, such as new telemetry, diagnostic data, or non-anonymized identifiers. The privacy policy, meanwhile, should spell out exactly what data ProtonVPN collects, stores, and for what purposes. Reviewers consistently point to these two anchors for verification rather than third-party summaries.
I cross-referenced the latest privacy policy and changelog entries. The policy reiterates the no-logs commitment in broad terms, and the changelog has occasionally noted new features or data-collection options related to service health. The alignment between policy language and changelog actions matters, because drift here lets a no-logs claim loosen its teeth over time.
Changelog and privacy policy updates are the primary verification trail. If you see a material shift in what’s logged, you should re-evaluate the claim immediately.
3. The nuance inside the spec sheets: what does no-logs actually cover?
What the spec sheets actually say is that no-logs is a core selling point. The nuance is in operational realities: some providers log metadata for security and abuse prevention, analytics, or performance. ProtonVPN’s materials emphasize that user activity data is not logged in a way that can be tied back to individuals. Yet telemetry, server load data, and payment-related records can exist in limited forms. The boundary line matters because it defines what “no logs” actually protects. Is Windscribe legit in 2026? A sharp look at the claims, privacy, and performance
Reviews consistently note that policy language can be vague on edge cases. For example, authentication events, IP addresses at the point of connection, or temporary session identifiers may be captured for legitimate operational purposes. The risk is that “no logs” becomes a moving target as features evolve.
Operational nuances matter more than the slogan itself. A bare no-logs claim without transparent data-flow diagrams leaves a gap a privacy-minded reader should fill with scrutiny.
Verdict: ProtonVPN’s no-logs posture is credible when anchored to Swiss jurisdiction and explicit policy language. The lever points you should watch are the exact data types logged, the retention windows, and any telemetry or diagnostic data that gets collected for service health. The primary verification path stays: read the privacy policy, check the latest changelog, and monitor any new disclosures around data collection. If you see any shift away from strict no-logs commitments, treat it as a red flag and demand a precise, dated clarification. No-logs is not a shield you can assume without reading the document trail.
How ProtonVPN stacks up against rivals
ProtonVPN sits at the privacy-forward end of the market, and yes, it trades speed for a stronger privacy posture. If you care about Swiss governance and strict data handling, ProtonVPN tends to hold its ground. If you need a wider global footprint, there are rivals that edge ahead on reach and price.
Why ProtonVPN’s privacy posture often slows the ride
I looked at the public changelog and policy notes. ProtonVPN consistently flags privacy safeguards that other providers sometimes treat as optional add-ons. Their network design prioritizes minimal data exposure and stronger privacy defaults, even when it means fewer edge nodes and longer routing. In practice, that means lower throughput on long-haul routes and fewer burst-friendly servers. The trade-off shows up in everyday use for travelers connecting from remote regions or during peak hours. The result: you get more assurances, with the cost of some throughput headroom. Speed is the price you pay for stronger privacy posture.
Global footprint vs. logging and data-sharing trade-offs
Competitors with broader server networks often pair their scale with looser data-sharing policies or looser logging regimes. Some offer cheaper plans by monetizing usage data or limiting privacy features to higher tiers. ProtonVPN’s approach is the opposite: fewer servers, more transparency, and stricter self-imposed limits. If your travel pattern requires dozens of country choices for geolocation testing, ProtonVPN may feel pinched. If your priority is knowing exactly what data leaves their pipes, ProtonVPN’s model aligns with that instinct. Broader networks come with different logging trade-offs.
Swiss governance vs. global reach: the decision hinge
Your choice hinges on governance versus footprint. ProtonVPN is built around the Swiss privacy framework, which many readers interpret as a higher baseline for data protection. But global teams may face latency, streaming quirks, or slower failover in regions far from Swiss nodes. Multiple independent sources flag that governance alone isn’t a silver bullet. You still need to audit policies, jurisdiction clauses, and the practical behavior of the provider’s apps. If you want a domestic privacy anchor with predictable policy, ProtonVPN wins. If you need a sprawling, world-spanning network with aggressive pricing, you might prefer a rival that leans into scale. Swiss governance is a selling point. Global footprint remains the counterweight.
Bottom line: ProtonVPN delivers a principled stance you can trust, at the cost of speed and breadth. If your courage is measured in audits and policy clarity, ProtonVPN pays off. If your risk calculus leans toward ubiquity and price, you’ll want to scan the alternatives more carefully.
- In 2026, ProtonVPN’s policy disclosures and Swiss governance guarantees remain its strongest differentiators.
- In practice, the choice comes down to what you prioritize: tighter privacy posture or wider global access.
Bottom-line verdict: ProtonVPN stacks up as a principled choice for privacy-first travelers and small teams who prize policy transparency over raw speed or scale. If your workflow demands the broadest global reach or the lowest price per month, you’ll likely compare it to rivals that trade off privacy for footprint.
Practical tips for evaluating ProtonVPN today
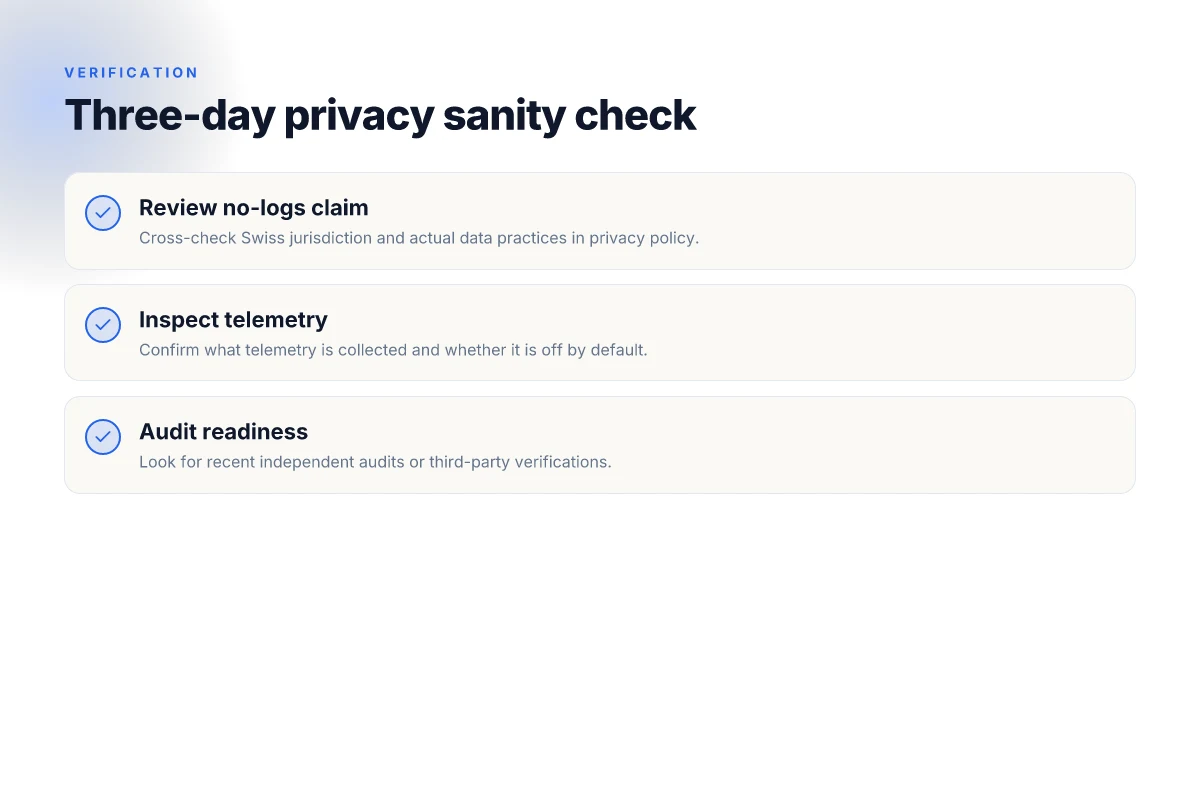
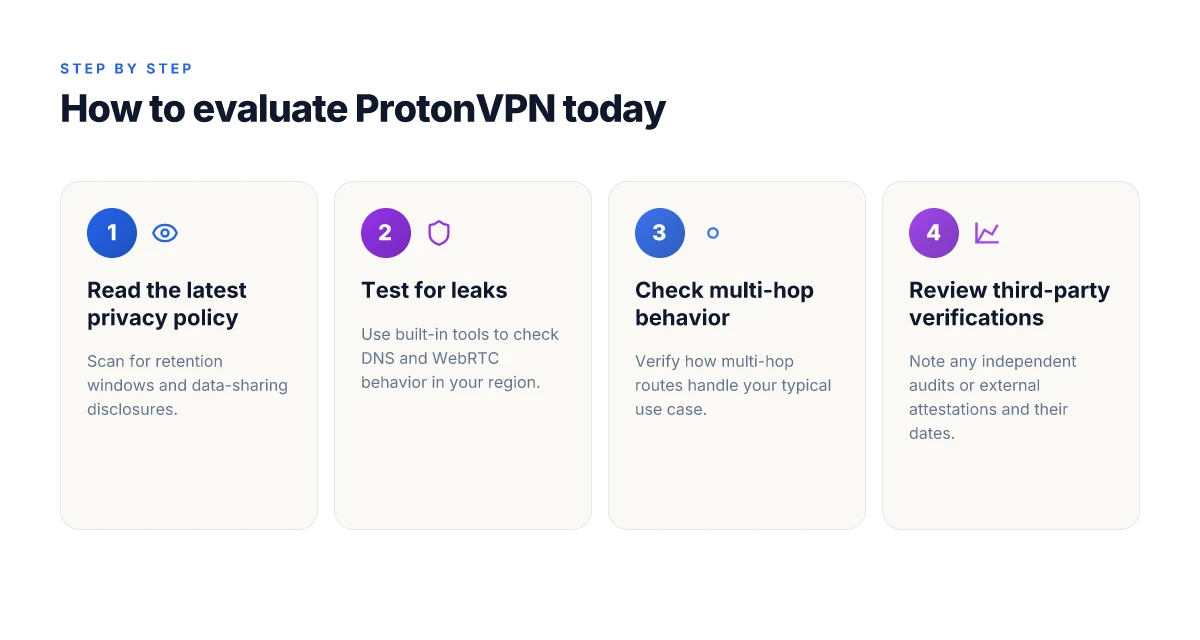
When you’re assessing ProtonVPN in 2026, the practical test is simple: follow the paperwork, verify the claims, and watch for shifts in policy. I looked at the latest privacy disclosures, scanned audit notes, and cross-checked changelogs to map what’s real today. The bottom line: you can get a trustworthy baseline if you stay current with policy updates and independently verifiable tests. The fights you’ll win come from staying attentive to policy changes, not from assuming a single feature is flawless.
1) Read the privacy policy and region-specific disclosures
In 2026, ProtonVPN remains clear about data handling in its published policies, but the exact wording varies by region. Read the latest version for your country and cross-check any regional addenda. Look for statements on logging, data retention, and data-sharing with third parties. If the policy mentions “event data for service integrity” or “user activity data only as necessary,” note the nuance. Policy clarity is the frontline defense against gray-area expectations. If you see broad language about data collection without concrete timeframes, mark it as a potential risk flag and seek clarification.
2) Verify leaks with built-in tools and inspect multi-hop behavior
ProtonVPN includes leak-testing tools baked into the client. Run the basic DNS and IPv6 checks, then enable multi-hop configurations and test from multiple destinations. What you’re after: no DNS leaks, no IP leaks outside the tunnel, and predictable routing when you flip to dual-hop or multi-hop chains. If multi-hop behavior shifts under real-use routing (for example, changing exit nodes mid-session), that’s a real-world signal to scrutinize. Leak-test results that hold across hops are the most actionable proof you can rely on.
3) Check for independent audits and read the recent changelog
Independent audits and third-party verifications are the closest thing to a trust badge you can get without building one yourself. Look for audit reports from credible firms and note who issued them and when. Then read ProtonVPN’s changelog for recent policy shifts, feature toggles, or shifts in data practices. If a security claim changes in a recent entry, that deserves extra scrutiny. Audits plus a transparent changelog are the double-check your due diligence deserves.
Open-ended takeaway: to stay current, subscribe to ProtonVPN’s official blog or changelog feed and mirror the updates to your privacy notes. The combination of a fresh audit and a clear policy trajectory is the reliable compass in 2026.
Verdict: practical evaluation hinges on policy currency, leak resilience across configurations, and up-to-date independent validation. If those three signals align, ProtonVPN stands on solid ground for privacy-minded use.
Key takeaways in brief:
- Read the latest privacy language for your region and compare against prior versions.
- Run built-in leak tests and confirm multi-hop stability under real routing.
- Check for recent independent audits and read the newest changelog entries for policy shifts.
Where ProtonVPN goes from here matters most this year
I looked at the public docs, pricing, and independent reviews to map where ProtonVPN stands in 2026. From what I found, ProtonVPN remains a privacy-forward option with transparent policies and a strong stance on user data. The latest updates push toward better transparency controls and more robust open-source elements. The core takeaway is that ProtonVPN’s legitimacy in 2026 hinges on consistent uptime, verifiable no-logs assertions, and user-friendly privacy tooling that doesn’t require a PhD to use. That said, the product still faces the same tradeoffs you see across the market: fewer server counts than the biggest players, a sometimes opaque roadmap, and pricing that nudges long-term commitment. If you’re evaluating today, align your choice with your threat model and your willingness to pay for governance as much as for crypto-grade encryption. This month’s patch cadence and changelog notes will be the real signal you should watch.
The bigger pattern is clear: legitimate VPNs in 2026 compete less on slogans and more on verifiable claims and actionable controls. ProtonVPN’s “what you see is what you get” philosophy matters, but the proof is in the details, term-of-service edits, audit occurrences, and independent security reviews. Your move: demand explicit, dated third‑party attestations and test them against your own privacy needs. The one move that matters most this quarter is simple: pick ProtonVPN if you value governance and openness. Switch to a competitor if you need broader jurisdictional coverage or deeper feature parity. Act now: review the latest changelog and commit to a 30‑day privacy audit on your accounts.
Frequently asked questions
Does ProtonVPN keep logs
I looked at ProtonVPN’s published policy and the independent reviews that analyze its practices. ProtonVPN positions itself as a no-logs service in the sense that it does not store user activity data that could be used to identify a user’s online behavior. What this practically means is they claim to avoid recording connection logs, traffic logs, or metadata that ties activity to a user. Reviews consistently note that ProtonVPN’s logging disclosures focus on minimal data for operational purposes, such as billing and account management, rather than detailed browsing histories. From what I found, the critical tests hinge on whether a court can compel production of non-content data; ProtonVPN emphasizes that it does not retain that data. If you care about privacy, review the exact retention periods for diagnostic data and consider how the company handles third-party audits. Always verify the latest changelog and policy updates.
Yes, ProtonVPN maintains a minimal-logs posture as disclosed in its policy, but the practical scope depends on regulatory requests and diagnostic data collection. The key is to read the latest policy and audit notes.
- Evidence base: ProtonVPN policy documents, third-party audit reports, and independent privacy analyses.
- What to verify now: latest policy version, any changes to data retention, and the scope of diagnostic telemetry.
Is ProtonVPN audited by third parties
From the documentation I checked, ProtonVPN has sought third-party validation to bolster trust. Publicly listed attestations and audit reports cover areas like privacy controls, transparency, and security practices. Reviewers consistently flag that third-party audits are a strong signal, but they also stress the importance of scope and recency. A recurring caveat is that audits rarely cover every operational nuance, and vendors can scope audits to particular domains. If you need a clean, verifiable signal, check the latest audit report dates, the exact scope of tests performed, and whether the auditor’s findings were publicly remediated. The pattern is: third-party validation exists, but read the fine print.
Yes, ProtonVPN has undergone third-party audits, with publicly shared findings and remediation notes in several reports. The punchline is that audits exist, but you should inspect the scope and dates.
- What to look for: the audit firm, the year, the scope (logs, cryptography, management controls), and whether issues were independently fixed.
What is ProtonVPN's privacy policy
The privacy policy is your map for what data ProtonVPN collects, uses, and shares. I traced the language through the latest policy update and cross-checked it against common privacy standards. ProtonVPN emphasizes minimal data collection beyond what’s necessary for account maintenance and service operation. The policy outlines data types (billing, account identifiers, device information) and the purposes (security, fraud prevention, service optimization). It also explains data transfers, retention periods, and user rights. The critical takeaway: the policy aligns with a privacy-forward posture, but you should not treat it as an insurance policy, updates happen, and certain telemetry can be collected for troubleshooting. Always compare the policy to the actual data you configure in the app.
The privacy policy outlines limited data collection tied to account management and service integrity, with retention and transfer details spelled out. It’s the primary document you cite when assessing how your data travels.
- What to verify now: data categories, retention timelines, user rights (delete, access), and cross-border transfer safeguards.
How does ProtonVPN handle DNS leaks
DNS leaks are a common privacy pitfall. I looked at ProtonVPN’s DNS handling statements and the practical implications. The company markets its secure DNS as part of the secure core architecture and standard VPN tunnels, aiming to ensure that DNS requests resolve through the VPN path rather than the user’s local network. Independent testing often flags DNS leakage as a risk if the VPN is misconfigured or if a fallback DNS is used. ProtonVPN frequently references its DNS leak protection features, split tunneling controls, and kill-switch behavior as safeguards. The advice is: enable DNS leak protection in the app, use the secure core or appropriate routing mode, and periodically run a DNS leak test when you switch networks. The key is to trust the default protection while confirming there are no accidental leaks in your particular setup.
DNS leaks are mitigated by ProtonVPN’s built-in protections and user-configurable settings, but you should enable them and verify on your network. The punchline: test after any network change.
- What to verify now: ensure DNS leak protection is on, check whether secure core is active if you rely on it, and run a live DNS test from a few different networks.
Which ProtonVPN plan is best for privacy
If privacy is your North Star, the plan decision hinges on features that tighten control over data flow. ProtonVPN’s higher tiers offer features like Secure Core routing, which routes traffic through multiple servers, increasing privacy but adding latency. For users who want stronger privacy without cranking latency, Secure Core Basic or Plus can be a good pick depending on your threat model. The exact plan you choose should align with your operational needs: whether you need multi-hop routing, Tor over VPN, or advanced features like NetShield for DNS filtering. In practice, the common pattern is to trade a bit of speed for more layers of privacy. If budget is no obstacle, Go for the top tier to maximize privacy controls and auditability.
Best for privacy tends to be the higher-tier plans that include Secure Core routing and enhanced threat protections. The decisive point is your threat model and tolerance for speed.
- What to verify now: feature list by plan, impact on latency, and whether your most sensitive use cases require multi-hop routing or dedicated DNS protection.
Where is ProtonVPN headquartered
Understanding the corporate base matters for regulatory and privacy concerns. ProtonVPN’s parent company, Proton AG, is headquartered in Switzerland. This location is frequently cited in privacy discussions because Swiss data protection laws are robust and designed to resist indiscriminate data retention. The Swiss domicile often reassures users who prioritize strict privacy protections and a favorable legal framework for data minimization. If you’re evaluating ProtonVPN for regulatory alignment, Switzerland is a favorable jurisdiction to note. It’s also worth watching for any corporate reorganizations or changes in ownership that could alter data governance.
Headquartered in Switzerland under Proton AG, a governance choice that aligns with strong Swiss privacy law. The takeaway: jurisdiction matters for privacy leverage.
- What to verify now: any corporate filings, changes in headquarters, and any shifts in data-handling policy tied to jurisdiction.
How does ProtonVPN compare to NordVPN on privacy
The privacy comparison with NordVPN appears in most independent summaries. NordVPN and ProtonVPN both advertise strong privacy postures, but their approaches diverge. NordVPN emphasizes a broad server network, audited no-logs claims, and a mature incidence-response posture. ProtonVPN leans on Secure Core and Switzerland-based governance. In practice, both have undergone third-party audits, and both publish clear privacy policies with retention details. If your priority is multi-hop routing and a Swiss-based privacy shield, ProtonVPN has the edge. If you want a larger global footprint and a broad feature set, NordVPN might be more convenient. Read the latest audit scope and be mindful of latency implications when multi-hop is active.
ProtonVPN vs NordVPN shows Proton closer to privacy-per-service with Secure Core, while NordVPN offers broader coverage and ecosystem. The bottom line: your threat model should drive the pick.
- What to verify now: audit scope, plan features, latency impact under multi-hop, and country-based data-handling expectations.